
Enterprise AI security, without the complexity
Every AI agent gets the same enterprise-level protection: strict access controls, full auditability and zero data retention at the LLM layer, whether it is answering a question or automating a workflow on its own.
Teams at 80+ companies use our platform


check out our reviews
Enterprise AI Security
Everything your team needs to run AI agents and automate workflows with confidence
🛡️
Dedicated, isolated tenant per customer
🚫
Zero data retention at the LLM layer
🔒
Encryption at rest and in transit
👥
Role-based access controls
📋
Full audit logs
🤖
Every AI agent's action is scoped and logged
🔄
Your data never trains AI models
🔑
SSO & SAML
Enterprise AI Architecture
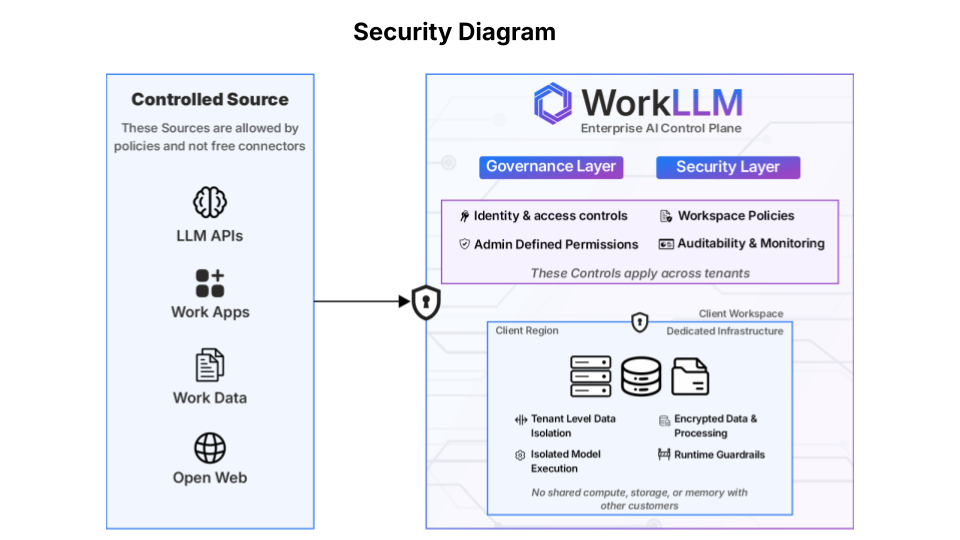
Dedicated tenant for every enterprise customer
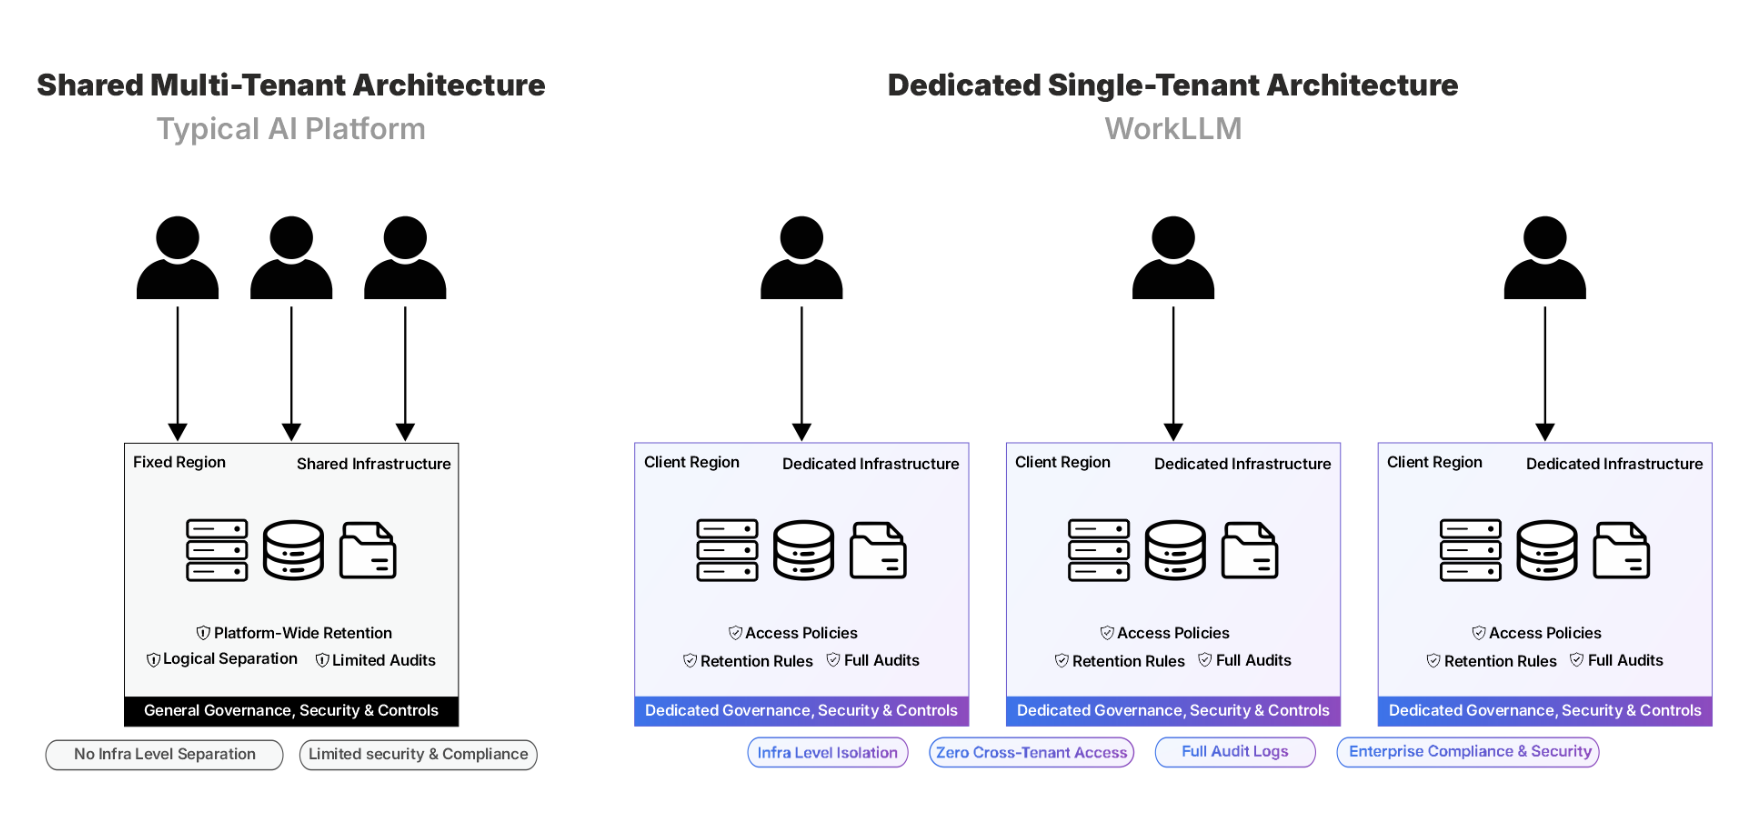
Every WorkLLM enterprise customer gets their own dedicated tenant, logically isolated at the application layer, including everything your AI agents do. Your data, your AI context, and your permissions live in a space that’s yours alone, never shared, never mixed with anyone else’s. Enterprise customers can go further with dedicated infrastructure-level isolation, a private VPC with your own servers and storage.
What this gives you
- No cross-tenant exposure: Your data never mixes with another customer’s, by design.
- Your own audit trail: Every workspace keeps its own activity logs and governance history.
- Deployment that fits you: Run in WorkLLM’s cloud or your own infrastructure, whichever your data rules require.
What's Isolated
- Your data: Conversations, documents, and metadata stay inside your tenant.
- Your AI context: Embeddings and retrieval are scoped to you, so nothing leaks across workspaces.
- Your access controls: Permissions and roles, including what each AI agent is allowed to access, are enforced independently for your workspace.
Enterprise AI Security at every layer, not bolted on after
Isolation, access controls, encryption, and oversight are built into the architecture, so every AI agent your team runs gets serious protection without the complexity, and your data never leaves your control.
Enterprise AI Security Controls
How your workspace stays secure?
Isolation is the foundation. These capabilities protect your data, and everything your AI agents do with it, across every layer of the workspace.
Encryption at rest and in transit
Your data is encrypted at rest and protected in transit using modern industry standards, so it's safe wherever it lives and moves.
Role-based access control (RBAC)
Granular permissions mean every user and service can access only what they're meant to, nothing more.
SSO and authentication
Secure sign-in with optional SAML-based SSO, so access fits how your team already logs in.
Audit logs and activity tracking
Every meaningful action is logged in your workspace, so you can review activity and answer questions with confidence.
Input and output guardrails
Redact sensitive data, restrict prompts, and keep outputs within your policies, automatically, across the workspace.
Your data never trains AI models
Customer data is never used to train models. It's processed only for the request at hand, never retained for training.
Zero data retention at the LLM layer
Requests to model providers aren't retained by them, giving you zero data retention at the LLM layer.
Full admin control
Admins manage integrations, sharing, usage visibility, and access from one place, so oversight stays central and every action, including everything an AI agent does, stays permission-scoped and logged.
FAQs
Is our data isolated from other customers?
Yes. Every WorkLLM customer is provisioned into their own dedicated tenant, logically isolated at the application layer, so there’s no cross-customer exposure, by design. Enterprise customers can additionally add infrastructure-level isolation with a dedicated private cloud.
Does WorkLLM use our data to train AI models?
No. Your data is never used to train models. Prompts are processed only for the request at hand and are never retained for training.
What does "zero data retention at the LLM layer" mean?
Requests to the model providers are processed transiently and aren’t retained by them, giving you zero data retention at the LLM layer.
Where is our data stored?
Your data is stored securely within your dedicated tenant, isolated from other organizations and accessible only to your workspace.
What access controls are available?
WorkLLM supports role-based access control (RBAC), so admins can define exactly what each user, assistant, agent, and integration can access.
Are user actions auditable?
Yes. Every meaningful action, access changes, configuration updates, and data usage, is logged and available to your workspace admins.
How is our data encrypted?
All data is encrypted at rest and protected in transit using modern, industry-standard encryption.
How does WorkLLM prevent unauthorized access?
Through authentication, role-based permissions, session management, and application-layer tenant isolation, with infrastructure-level isolation available for Enterprise customers.
Do you offer on-premise deployment?
Yes. WorkLLM can run in our managed cloud, your private VPC, or fully on-premise, depending on your security and data residency requirements.
Can WorkLLM be deployed in our own infrastructure?
Yes. We support dedicated deployments inside your own environment for stricter regulatory or data residency needs.
How can our security team get more information?
We’re explicit about how your data is processed, stored, and protected, no vague claims, no hidden behavior, just clear answers your security, legal, and IT teams can rely on. Send your questions or security questionnaire to hello@workllm.io and we’re happy to support your review.
Can I control what an AI agent is allowed to do?
Yes. You choose exactly which tools and integrations an AI agent can access, and whether it runs fully automatically or holds for your approval before each action.
Are an AI agent's actions logged separately from chat activity?
Yes. Every action an AI agent takes is recorded in your workspace’s audit log, the same governance and audit trail that covers everything else in WorkLLM.
Can I pause or disable an AI agent if something looks wrong?
Yes. You can pause or disable any AI agent at any time from your workspace settings, immediately stopping it from taking further action.
Automate your processes through AI agents without giving up control
Tenant isolations, strict access controls, and zero data retention at the LLM layer, so your data stays yours while you automate your workflows through AI Agents